


A VoIP STUN server is a lightweight discovery service that tells a SIP client which public IP address and port its traffic appears to come from after passing through a NAT router. It solves the single most common cause of failed VoIP calls, which is one-way or no audio caused by unreachable private addresses. If STUN alone cannot establish the connection, a TURN relay or a managed platform like VideoSDK, which handles NAT traversal internally, completes the picture.
Introduction
Every VoIP engineer eventually hits the same wall: calls connect, the phone rings, and then there is silence. The signaling worked, but the media did not. In the majority of these cases the culprit is Network Address Translation (NAT). A VoIP phone sitting behind a home or office router advertises its private address, such as an address in the 192.168.x.x range, inside its SIP messages and media descriptions. The remote endpoint tries to send audio to that address, the packets go nowhere, and the call fails.
This is precisely the problem a voip stun server exists to solve. STUN, short for Session Traversal Utilities for NAT, lets a client discover its public-facing address before the call is set up, so the addresses it advertises are actually reachable. It is one of the oldest and most reliable building blocks in real-time communication, standardized by the IETF and used by virtually every WebRTC and SIP stack in production today.
In this guide you will learn what a STUN server actually does, how the protocol works under the hood, how to choose and deploy one, and how to integrate it with SIP proxies, PBXs, and softphones. We will also cover the cases where STUN is not enough and you need TURN or a managed real-time communication platform.
What Is a VOIP STUN Server?
A VoIP STUN server is defined as a network service that helps a VoIP or SIP client discover the public IP address and port that a NAT device has assigned to its connection. The client sends a short request to the STUN server over UDP or TCP, and the server replies with the address it observed as the source of that request. Because the server sits on the public internet, what it sees is the address the rest of the world sees.
STUN works by exploiting a simple asymmetry: the client cannot see its own public address, but any external observer can. The protocol is intentionally minimal. There is no session state, no media forwarding, and no encryption of the discovery exchange itself in the base protocol. A single request and response, typically well under 100 bytes each, is all it takes.
The current protocol specification is RFC 8489, published by the IETF, which consolidated the earlier RFC 5389 and clarified authentication, error handling, and IPv6 behavior. Any modern STUN implementation you deploy or integrate should claim compliance with RFC 8489.
A useful analogy comes from managed communication platforms. When you join a VideoSDK room, the SDK performs address discovery and connectivity checks on your behalf so that two participants behind different NATs can exchange media without either of them configuring anything. A STUN server is the raw, self-managed version of that first discovery step. Platforms like VideoSDK bundle STUN, TURN, and media routing into one service, while a standalone STUN server gives you the same discovery primitive to wire into your own SIP infrastructure.
How STUN Works Under the Hood
The STUN protocol is a simple request-response exchange built from binary messages with typed attributes. A client behind NAT sends a binding request to the server, and the server responds with a binding response containing the observed source address.
The classic attribute carrying that address is MAPPED-ADDRESS, which reports the public IP and port of the client as seen by the server. Modern implementations rely on XOR-MAPPED-ADDRESS instead, an extension introduced in RFC 5389 and retained in RFC 8489 that XORs the address with a fixed magic cookie. The XOR encoding exists because certain legacy NAT devices intercepted and rewrote plain IP addresses found in packet payloads, corrupting discovery. XOR-MAPPED-ADDRESS defeats that rewriting, and both attributes are usually included for compatibility.
Transport matters more than developers expect. STUN runs natively over UDP, which is the natural fit for real-time media, but it also runs over TCP and over TLS, and over DTLS when used as part of the ICE framework in WebRTC. The default port for both UDP and TCP STUN is 3478, a well-known port registered with IANA. When STUN is multiplexed with DTLS, as in WebRTC candidate exchange, port 3479 is used.
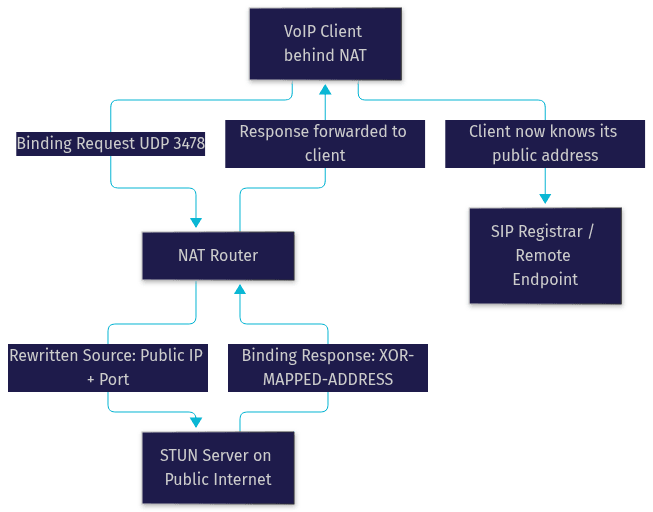
One important limitation: STUN only discovers the address. It does not open a path through the NAT by itself. Whether the discovered address actually works for incoming media depends on the NAT type. For symmetric NATs, the most restrictive common type, the port mapping observed by one STUN server will not match the mapping used toward a different destination, so the discovered address is useless for direct media exchange. That is why the ICE framework pairs STUN with TURN, and why production VoIP architectures always plan for a TURN fallback.
Choosing the Right STUN Server for Your VoIP Architecture
Selecting a STUN server comes down to four criteria: protocol compliance, IPv4 and IPv6 support, scalability, and observability.
On the open-source side, several mature implementations exist. Stuntman is a widely deployed C++ STUN server known for stability and dual-stack support. Node-based STUN implementations suit teams that want a lightweight service embedded in an existing Node.js infrastructure. Many TURN server packages, including the popular coturn project, also bundle a full STUN implementation, which is convenient because most production deployments eventually need both on the same host.
Hosted public STUN services from Google, Twilio, and Cloudflare are free to use and globally distributed, which makes them attractive for client-side discovery in consumer apps. The tradeoff is control: you get no logging, no SLA guarantees for discovery specifically, and no ability to co-locate STUN with your own TURN relay. For enterprise VoIP, self-hosting STUN next to your TURN server on the same public address is the standard pattern, because ICE candidates work best when discovery and relay share infrastructure.
| Option | Type | IPv4/IPv6 | Best For |
|---|---|---|---|
| Stuntman | Open source | Both | High-volume self-hosted discovery |
| coturn (STUN mode) | Open source | Both | Unified STUN + TURN deployments |
| Node-based STUN | Open source | Varies | Embedding in Node.js services |
| Google STUN | Hosted, free | Both | Consumer client-side discovery |
| Cloudflare STUN | Hosted, free | Both | Globally distributed low-latency discovery |
| Twilio STUN | Hosted, free | Both | Apps already using Twilio |
[LINKABLE ASSET — comparison table]
Whichever you choose, verify RFC 8489 compliance in the documentation, confirm dual-stack support if your network runs IPv6, and check whether the implementation exposes response-time metrics you can feed into monitoring.
Deploying a VOIP STUN Server: Practical Steps
Deploying a STUN server is one of the shorter infrastructure projects you will run, but the production details are where deployments succeed or fail. The lifecycle below covers the full path from host selection to verification.
Step 1: Select the Host
Choose between a virtual machine, a container, or a serverless-friendly setup. A VM or container with a public IP address is the standard choice, because STUN must be reachable directly from the open internet. Place the server geographically close to your VoIP users, since every STUN query adds a round trip to call setup time. A server in the same region as your SIP infrastructure keeps that latency in the low single-digit milliseconds.
Step 2: Configure Network Interfaces
The server needs at least one interface bound to a public IP. For dual-stack deployments, bind separate listeners on the IPv4 and IPv6 addresses. Many implementations support a primary and an alternate IP address on the same host, which is useful for NAT type detection: a client that queries two different addresses can compare the mappings and detect whether it sits behind a symmetric NAT.
Step 3: Set Primary and Alternate Ports
Configure the primary listener on UDP port 3478 and a second listener on an alternate port, commonly 3479 or a custom high port. The alternate listener serves the same NAT-detection purpose as the alternate IP. If your firewall policy restricts well-known ports, any high UDP port works, as long as your clients are configured to use it.
Step 4: Expose UDP and TCP
Open the chosen ports for both UDP and TCP transport. UDP is what most SIP clients will use, but TCP support matters for clients on restrictive networks that block UDP. Remember that stateful firewalls and NAT devices themselves must permit the return traffic, which they normally do automatically for outbound-initiated flows.
Step 5: Secure the Service
A pure STUN server exposes no data and holds no session state, so its attack surface is small, but it is still an internet-facing service. Restrict access at the firewall layer to the IP ranges of your actual users where possible, rate-limit requests to blunt abuse and reflection attacks, and if you run STUN alongside TURN, keep the TURN credentials and long-term authentication configuration strict. For encrypted discovery, STUN over DTLS is the standard option, and it is required when STUN is used inside WebRTC ICE.
Step 6: Test with a Public IP Discovery Tool
Verify the deployment by querying the server from a client behind NAT and confirming the returned address matches the public IP of that network. Test from multiple network types, including a symmetric NAT environment such as many corporate firewalls, and from an IPv6 network if you enabled it. A successful test returns the correct public address within a few milliseconds.
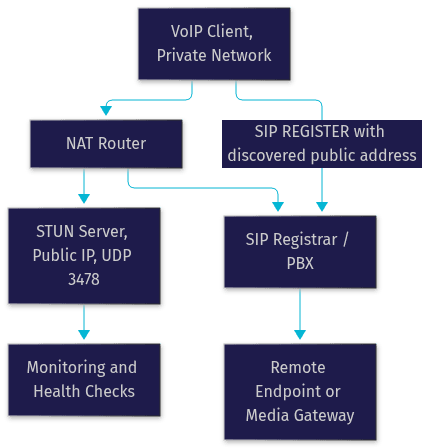
For production, plan for high availability from day one. Run at least two STUN instances behind a load balancer or advertised as multiple server entries in client configuration, so a single instance failure does not stall call setup. Monitor response time and packet loss continuously, because a slow STUN server directly delays every call's connection phase.
Integrating the STUN Server with SIP and VoIP Systems
Integration is where discovery meets the rest of your VoIP stack. SIP proxies, PBXs, and softphones all consume the STUN result differently, and mismatches here produce the classic one-way audio bug.
Most SIP clients and PBX engines expose a stun_server configuration parameter where you specify the address and port of your server. When the client registers with the SIP registrar, it first performs a STUN binding request, learns its public address, and then places that address into the Contact header and the media description of the SIP exchange. The registrar and the remote endpoint now have a reachable address to send signaling and media toward.
Systems with multiple network interfaces need extra care. Servers with several NICs often support primaryip and alternateip settings, letting you pin which interface the STUN binding uses. If the binding goes out the wrong interface, the discovered address will not match the interface carrying media, and calls will fail despite a successful STUN response.
Two pitfalls account for most integration failures. First, mismatched ports: the client advertises the media port it expects to use, but the NAT mapping discovered via STUN was opened toward the STUN server, not toward the media endpoint, so the mapping may differ. Second, NAT hairpinning: two clients behind the same NAT trying to reach each other via their public addresses. Many routers do not support hairpin routing, so internal calls between colleagues in one office fail even though external calls work. The fix is split DNS or local media bypass, where internal calls use private addresses directly.
If you are building real-time communication into an application rather than operating a traditional PBX, a managed platform removes this entire class of problem. VideoSDK's real-time communication SDKs handle STUN, TURN, and media routing automatically across ten platforms including React, Flutter, Android, and iOS, so participants behind any NAT topology connect without manual traversal configuration. For teams that need SIP interop as well, VideoSDK's telephony and SIP integration bridges traditional phone infrastructure into the same managed rooms.
Monitoring, Troubleshooting, and Performance Tips
A STUN server is small, but when it fails, every call setup in your system degrades. Treat it as a first-class monitored service.
Your health-check checklist should cover four items. Response time: a healthy STUN round trip should complete in under 50 milliseconds from the same region, and sustained increases indicate network or load problems. Packet loss: STUN over UDP is sensitive to loss, and a query that never returns forces client retries that delay call setup. Binding success rate: track the ratio of successful binding responses to requests, since a drop usually means firewall changes or interface misconfiguration. Port reachability: verify both UDP and TCP listeners from outside your network, because internal tests cannot detect edge firewall drift.
Log analysis focuses on patterns rather than individual requests. A spike in requests from a single source suggests a misconfigured client stuck in a retry loop. Requests arriving with no valid binding response often indicate a listener bound to the wrong interface. Error responses with a 400-class code point to malformed messages from a non-compliant client, while authentication errors only appear if you enabled the optional authentication mechanism from RFC 8489.
For scaling, run a load-balanced cluster of STUN instances and advertise multiple servers in client configuration. Because STUN is stateless, any instance can answer any query, which makes horizontal scaling trivial. The main scaling constraint is not CPU but network throughput and port availability on the NAT side of your users.
Finally, measure the latency impact on call setup. Every STUN query adds one round trip before registration or media negotiation begins. With a regional server this is negligible, but with a distant or overloaded server it can add hundreds of milliseconds to every call. Keep STUN close to your users, and your call setup times stay fast.
Definitions Glossary
STUN Server: A public internet service that tells a client behind NAT which public IP address and port its traffic appears to originate from, per RFC 8489.
NAT Traversal: The set of techniques, including STUN, TURN, and ICE, that allow two endpoints behind NAT routers to discover each other and exchange media directly.
XOR-MAPPED-ADDRESS: The STUN response attribute that reports the client's public address with the address bits XORed against a fixed magic cookie, preventing legacy NAT devices from rewriting the value.
ICE Framework: The Interactive Connectivity Establishment standard that pairs STUN discovery with TURN relaying to systematically test candidate address pairs and pick the best working path for media.
TURN Server: A relay service used when STUN discovery is insufficient, typically behind symmetric NATs, where media is forwarded through the server rather than exchanged directly.
SIP Registrar: The server component that accepts SIP registration requests and records the address at which a user can be reached, often populated using the address discovered via STUN.
Key Takeaways
- A VoIP STUN server solves the most common cause of failed VoIP calls by letting clients behind NAT discover and advertise their public IP address and port before media negotiation begins.
- The protocol is defined in RFC 8489, uses a single binding request and response, defaults to UDP port 3478, and relies on the XOR-MAPPED-ADDRESS attribute to survive address-rewriting NAT devices.
- STUN alone cannot traverse symmetric NATs or guarantee media flow, so production architectures pair it with TURN relays or use managed platforms like VideoSDK that handle STUN, TURN, and media routing automatically.
- Deployment success depends on public IP binding, dual-stack listeners, exposed UDP and TCP ports, firewall security, and high-availability clustering with continuous response-time monitoring.
- Integration pitfalls such as mismatched ports, wrong-interface bindings, and NAT hairpinning cause most one-way audio bugs, and each has a known fix in client and network configuration.
Conclusion
A reliable voip stun server is a small piece of infrastructure with an outsized effect on call quality. Get discovery right, and calls connect with audio in both directions. Get it wrong, and no amount of codec tuning will save the experience. The path is straightforward: choose an RFC 8489-compliant implementation, deploy it close to your users with high availability, integrate it carefully with your SIP stack, and monitor response time and packet loss as part of your routine health checks.
If you would rather not operate traversal infrastructure at all, VideoSDK's real-time communication SDKs handle STUN, TURN, and media routing for you across ten platforms, with a free tier to get started at app.videosdk.live. You can explore the full documentation at docs.videosdk.live, browse code samples, or join the VideoSDK Discord community to compare notes with other developers building real-time communication systems.
What are you building with STUN or managed RTC? Drop a comment, I'd love to hear what kind of NAT traversal scenario you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ