


WebSocket SSH is the technique of tunneling Secure Shell traffic through a WebSocket connection so a browser can act as a fully interactive remote terminal. Because WebSocket provides a persistent, full-duplex channel over HTTPS, developers get low-latency SSH access without installing a native client. This guide covers the architecture, setup, authentication, and security of SSH over WebSocket, plus where WebAssembly clients are heading in 2026.
Every developer has been there: you are on a locked-down machine, a borrowed laptop, or a tablet, and you need a shell on a production server right now. Installing PuTTY or firing up a native terminal is not an option. This is exactly the gap WebSocket SSH fills. By carrying SSH traffic over a WebSocket connection, the browser becomes a legitimate terminal client, complete with interactive shells, key authentication, and persistent sessions. The pattern has grown from a curiosity into a production technique used by cloud IDEs, web-based ops consoles, and remote support tooling. In this article, you will learn how SSH over WebSocket works under the hood, how to set up a browser-based SSH client, how to secure the channel properly, and what pitfalls to avoid along the way.
What Is WebSocket SSH?
WebSocket SSH is defined as the transport of SSH protocol traffic inside a WebSocket connection, typically secured with TLS (the WSS scheme), so that a web browser can originate and interact with an encrypted remote shell session. WebSocket is a standardized, persistent, full-duplex channel that begins life as an HTTP handshake and then upgrades to a long-lived binary connection. SSH, meanwhile, is the venerable protocol for encrypted remote command execution, port forwarding, and file transfer.
WebSocket SSH works by wrapping SSH packets inside WebSocket frames. A server-side bridge accepts the WebSocket connection, unwraps the frames, and forwards the raw SSH bytes to a local or remote SSH daemon. From the SSH server's point of view, nothing has changed: it still sees a normal SSH session with normal key exchange and encryption.
Typical use cases include browser-based SSH clients for cloud workstations, web terminals embedded in admin dashboards, SSH access from restricted corporate networks where only HTTPS egress is allowed, and persistent terminal sessions that survive page reloads. Because WebSocket traverses the same ports and infrastructure as ordinary web traffic, it slips past firewalls that block the traditional SSH port.
How WebSocket SSH Works Under the Hood
The end-to-end flow of WebSocket SSH follows a consistent pattern: the browser establishes a WebSocket connection to a bridge, the bridge opens a real SSH connection to the target host, and the two channels are then spliced together byte for byte. Every keystroke you type travels down the WebSocket as a binary frame, is translated by the bridge into SSH channel data, and is delivered to the remote shell. Output from the shell makes the reverse trip.
The critical property is that the SSH protocol itself is not modified. The bridge performs transport translation, not protocol translation. The browser-side client (usually a JavaScript terminal emulator paired with a WebSocket client, or increasingly a WebAssembly SSH implementation) handles the SSH encryption layer, so end-to-end confidentiality is preserved even though an intermediary relay exists.
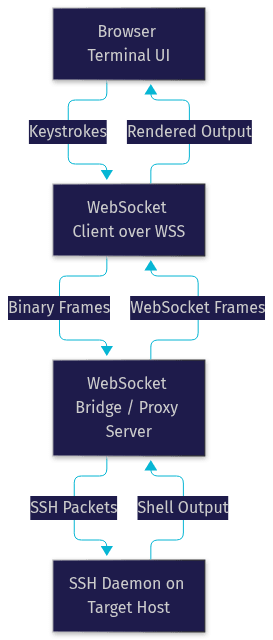
This bidirectional splicing is what makes the experience feel native. There is no polling, no request-response cycle, and no artificial latency floor. The moment the remote shell emits a byte, it is on its way back to your browser.
The Role of a Proxy or Bridge
A server-side component is unavoidable in the classic WebSocket SSH architecture because browsers cannot open raw TCP connections to arbitrary hosts. The bridge serves three functions. First, it terminates the WebSocket connection, accepting the upgraded HTTP request and maintaining the persistent channel. Second, it acts as a TCP client toward the SSH daemon, opening a real socket on the standard SSH port. Third, it relays bytes in both directions with minimal transformation, preserving SSH's own encryption end to end.
The bridge also handles practical concerns: connection lifecycle management, idle timeouts, reconnection logic, and access control. In production deployments, the bridge is where you enforce who may connect to which host, typically by validating a signed token issued by your application backend before the WebSocket handshake completes.
Setting Up a Browser-Based SSH Client
Building a browser-based SSH client involves four broad phases: choosing your client approach, wiring up the WebSocket endpoint, handling authentication, and rendering the terminal. Here is the path most teams follow.
Step 1: Choose your client architecture. You have two main options. The first is a JavaScript terminal emulator paired with a server-side bridge that speaks SSH on your behalf; the browser sends raw keystrokes and the bridge holds the SSH session. The second is a WebAssembly SSH client that implements the SSH protocol entirely in the browser and uses the WebSocket purely as a byte pipe. The first is faster to ship; the second offers stronger end-to-end security because your SSH keys never leave the browser.
Step 2: Configure the WebSocket endpoint. Your bridge exposes a WSS endpoint, usually behind the same reverse proxy that serves your application (Nginx, Caddy, or a CDN such as Cloudflare). The endpoint should require an authentication token as part of the initial handshake, and the proxy must be configured to allow long-lived connections with generous idle timeouts, since an interactive shell can sit quiet for minutes while a user reads output.
Step 3: Handle authentication. Decide whether credentials are supplied by the user through the terminal UI (password or key passphrase prompts rendered in the browser) or injected server-side by the bridge using pre-provisioned keys. For team tooling, server-side keys with per-user audit logging is the common pattern; for personal clients, browser-held keys are safer.
Step 4: Launch the terminal UI. Render an interactive terminal in the browser, attach it to the WebSocket's incoming byte stream, and forward user input as outgoing frames. Handle window resize events so the remote shell's line wrapping matches the visible terminal geometry.
After completing these steps, you should have a working browser terminal: type a command, press enter, and see output appear within milliseconds. If output lags by seconds, the problem is almost always proxy buffering or an idle timeout somewhere in the chain, not the WebSocket itself.
Common Errors and Fixes
The most frequent failure is the WebSocket handshake being rejected, usually caused by the reverse proxy not forwarding the upgrade headers. The second is silent session drops after roughly 60 seconds of inactivity, which points to a proxy or load balancer idle timeout that needs raising. The third is authentication loops, typically caused by the bridge and the browser client disagreeing on who owns the SSH handshake. Diagnose each by checking proxy logs first, since the bridge rarely sees the failure.
Authentication Methods for SSH over WebSocket
Authentication in WebSocket SSH happens at two layers, and both must be right. The outer layer authenticates the WebSocket connection itself; the inner layer authenticates the SSH session.
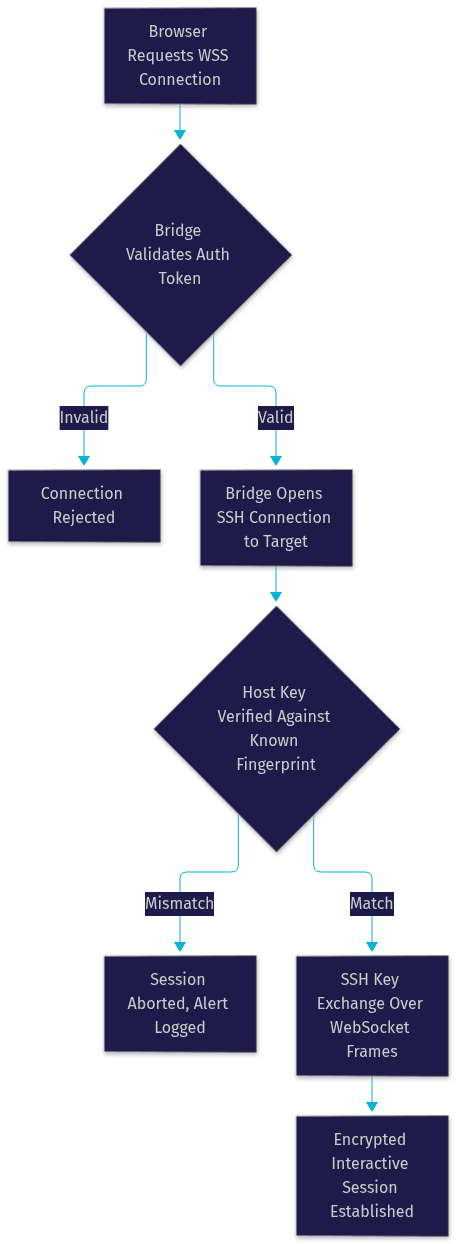
For the outer layer, the standard approach is a short-lived signed token attached to the WebSocket handshake. Your backend issues the token after the user logs into your application, and the bridge validates it before accepting the connection. This prevents random internet users from opening relay connections through your infrastructure.
For the inner layer, the usual SSH methods apply. Password authentication works but is discouraged for the same reasons it is discouraged everywhere. Public-key authentication is the norm: the user's private key either lives in the browser (in a WebAssembly client, ideally backed by WebCrypto non-extractable keys) or on the bridge server (in the relay model). Two-factor authentication integrates naturally, since the SSH challenge prompt simply renders in the browser terminal and the user types the one-time code as they would in any SSH client.
The key design rule: never send raw passwords or private key material as WebSocket message payloads in a custom format. Let SSH's own authentication exchange do the work, encrypted by SSH itself, so the WebSocket layer never needs to see credentials.
Security Considerations for WebSocket SSH
Security is where WebSocket SSH deployments most often go wrong, because developers secure the WebSocket and forget that SSH has its own trust requirements. A secure setup needs four things: TLS everywhere, host-key verification, token-gated access, and replay protection.
TLS is non-negotiable. Always use the WSS scheme so the WebSocket runs over HTTPS. Without TLS, keystrokes (including passwords typed into the terminal) are visible to anyone on the network path. Most deployments terminate TLS at a reverse proxy or CDN and run plain WebSocket internally, which is acceptable if the internal hop is on a private network.
Host-key verification is the step people skip. When the SSH connection is made from a bridge server, the bridge must verify the target host's SSH host key against known fingerprints, exactly as a native client would. If the bridge accepts any host key, you have built a machine-in-the-middle vulnerability: an attacker who can influence the bridge's network path can impersonate the target server. Browser-side WebAssembly clients should surface the host-key fingerprint to the user for confirmation on first connect.
Token-based access control closes the relay to outsiders. Issue short-lived, audience-scoped tokens that name the specific target host and user, and reject handshakes without them. This also gives you an audit trail.
Replay and man-in-the-middle protection comes from combining all of the above: TLS protects the outer channel, SSH's built-in key exchange protects the inner channel, and token expiry prevents captured handshakes from being replayed later.
One more consideration: rate-limit connection attempts at the bridge. Because the WebSocket endpoint is internet-facing, it will be scanned. Throttling failed handshakes per source IP keeps your logs clean and your attack surface small.
Performance and Latency of WebSocket SSH
WebSocket's persistent, full-duplex nature is precisely what makes browser SSH feel responsive. A traditional HTTP-based approach would require polling: the browser asks for new output every few hundred milliseconds, adding both latency and wasted requests. WebSocket eliminates that entirely. Once the connection is established, there is no per-message handshake overhead; frames are sent the moment data exists.
In practice, the dominant latency component is network round-trip time, not protocol overhead. A well-deployed WebSocket SSH setup adds only a few milliseconds of bridging cost on top of a direct SSH connection. The caveats are proxy buffering (some proxies batch small frames, which ruins interactive feel; disable buffering for the WebSocket route) and CDN hops, which can add tens of milliseconds depending on where the bridge is located relative to the target server. Place the bridge close to your SSH targets, not close to your users, because SSH traffic volume is tiny and round trips dominate.
Common Pitfalls and How to Avoid Them
Even a well-architected WebSocket SSH deployment hits a predictable set of problems. Here are the ones that cause the most pain, and how to mitigate each.
Token expiration mid-session. If your access token expires after a fixed window, long-running sessions can be killed abruptly. Mitigate by validating the token only at handshake time and letting established sessions run, or by refreshing tokens in the background before expiry.
Firewall and proxy interference. Some corporate proxies strip WebSocket upgrade headers or block long-lived connections. Mitigate by supporting a fallback transport (such as HTTP-based streaming) or by routing through a CDN that terminates WebSocket close to the user, since CDN-origin connections are rarely blocked.
Browser WebSocket limits. Browsers cap concurrent WebSocket connections per domain, typically around half a dozen to a couple of dozen depending on the browser. If your dashboard opens one WebSocket per SSH tab, heavy users will hit the cap. Mitigate by multiplexing several SSH sessions over a single WebSocket connection.
Session persistence across page reloads. A page refresh normally destroys the WebSocket and the SSH session with it. Mitigate by detaching the SSH session from the WebSocket: keep the session alive on the bridge for a grace period, and let the browser reattach with a session identifier. This is the same pattern tmux and screen solve natively, implemented at the bridge layer.
Idle disconnects. Proxies and load balancers close quiet connections. Enable WebSocket keep-alive pings at an interval shorter than the shortest timeout in your chain, and make sure your terminal renders the disconnect visibly rather than silently freezing.
Choosing the Right WebSocket SSH Implementation
There is no single right way to deploy WebSocket SSH; the right choice depends on scale, security posture, and how much infrastructure you want to own.
Self-hosted bridges give you maximum control. You run the WebSocket-to-SSH relay on your own servers, behind your own TLS, with your own access policies. This is the right choice when targets are private hosts that must not be reachable from third-party infrastructure, or when compliance requires it. The cost is operational: you maintain the bridge, its updates, and its security.
Edge and serverless platforms, including Cloudflare Workers with WebSocket support, let you run the bridge at the network edge with zero server management. This works well for low-volume, personal, or team tooling where the target hosts are publicly reachable. Watch the platform's execution-time and connection-duration limits, since interactive SSH sessions can outlive typical serverless budgets.
Open-source projects occupy the middle ground: established browser SSH tools and tunneling utilities give you a tested bridge and terminal UI without writing your own. Evaluate them on three criteria: whether the bridge verifies host keys, whether sessions can survive reconnects, and how actively the project is maintained.
For most teams starting out, the pragmatic path is an open-source bridge self-hosted behind an existing reverse proxy, promoted later to a multiplexed, session-persistent architecture as usage grows.
Future Trends: WebAssembly SSH Clients
The most significant shift underway in 2026 is the move toward WebAssembly SSH clients that run the entire SSH protocol inside the browser. In this model, the WebSocket becomes a dumb byte pipe, and the browser performs the SSH handshake, key exchange, and encryption locally. The server-side bridge shrinks to a minimal TCP relay, or disappears entirely when combined with edge functions that forward raw bytes.
The security implications are substantial. Your private key can be generated and stored in the browser as a non-extractable WebCrypto key, meaning no server component ever touches your credentials. Host-key verification happens in front of the user, restoring the same trust model as a native client. Performance is also improving as WASM execution approaches native speed for cryptographic workloads.
The remaining friction is key management across devices and the maturity of the tooling. But the direction is clear: browser SSH is evolving from a relayed convenience into a first-class, end-to-end encrypted client.
Definitions Glossary
WebSocket SSH: The technique of carrying SSH protocol traffic inside a WebSocket connection so a browser can serve as an interactive remote terminal.
WebSocket (WSS): A persistent, full-duplex communication channel that begins as an HTTP handshake; WSS is the TLS-encrypted variant, equivalent to HTTPS for WebSockets.
SSH (Secure Shell): A cryptographic network protocol for encrypted remote command execution, port forwarding, and file transfer between a client and a server.
Bridge / Proxy: The server-side component that terminates the WebSocket connection and relays bytes to and from a real SSH daemon over TCP.
Host-Key Verification: The process of checking a server's SSH identity fingerprint against a known value, preventing man-in-the-middle impersonation of the target host.
WebAssembly SSH Client: A browser-based SSH implementation compiled to WebAssembly that runs the full SSH protocol, including encryption and key handling, entirely client-side.
Key Takeaways
- WebSocket SSH tunnels SSH traffic through a persistent, full-duplex WebSocket connection, letting a browser act as a fully interactive remote terminal without a native client.
- A server-side bridge is required in the classic architecture because browsers cannot open raw TCP sockets; it translates WebSocket frames into SSH packets while preserving SSH's end-to-end encryption.
- Security requires four layers working together: TLS on the WebSocket, host-key verification at the SSH layer, short-lived tokens gating the bridge, and rate limiting on the public endpoint.
- The most common production failures are proxy idle timeouts, handshake header stripping, and lost sessions on page reload; all have well-understood mitigations.
- WebAssembly SSH clients are shifting the model toward full in-browser SSH, where the WebSocket is just a byte pipe and private keys never leave the client.
Conclusion
WebSocket SSH turns the browser into a serious terminal client, combining SSH's proven encryption with WebSocket's low-latency, firewall-friendly transport. The architecture is simple at its core, a bridge splicing two byte streams, but production quality lives in the details: TLS, host-key verification, token-gated access, and sessions that survive reconnects. Start with an open-source bridge behind your existing reverse proxy, harden the handshake, and keep an eye on WebAssembly clients as they mature. If your project also needs embedded real-time communication beyond terminals, such as video calling or interactive live streaming, explore VideoSDK's real-time communication SDKs and the VideoSDK blog for more developer guides. What are you building with WebSocket SSH? Drop a comment, I'd love to hear what kind of browser terminal use case you are working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ