


A STUN server is a lightweight protocol service that helps a device discover its public IP address and port as seen from the internet, enabling NAT traversal for peer-to-peer connections in WebRTC, VoIP, and SIP applications. It works by reflecting a client's network address back to them, without relaying any media. STUN alone succeeds for most NAT types, but restrictive NATs and corporate firewalls require a TURN server as a relay fallback. VideoSDK handles this entire connectivity layer for you, so you can focus on your application instead of infrastructure.
Every WebRTC developer eventually hits the same wall: two peers that can reach the internet but cannot reach each other. The culprit is almost always Network Address Translation, the router-level technology that hides devices behind a shared public IP. The STUN server is the first and most important tool for solving this problem, and understanding it deeply will save you countless debugging hours.
This guide covers what a STUN server actually does, how it fits into the ICE connectivity process, how to choose and configure one, and when to give up on STUN and bring in a TURN relay. By the end, you will know exactly where STUN fits in a production real-time communication stack.
What Is a STUN Server?
A STUN server is defined as a network service implementing the Session Traversal Utilities for NAT protocol, standardized in RFC 5389 and refined in RFC 8489, whose job is to tell a client what its public IP address and port look like from the outside. STUN stands for Session Traversal Utilities for NAT, and despite the acronym, the protocol itself is remarkably simple: the client sends a request, and the server responds with the source address it observed.
STUN works by receiving a UDP packet on a known port (typically 3478), inspecting the source address of that packet, and echoing it back in the response. When your device behind a NAT sends that request, the NAT rewrites the packet with its own public IP and an allocated port. The STUN server sees the rewritten address, not your local one. That reflected address, called a server-reflexive candidate or SRFLX candidate, is what your peer can potentially use to reach you.
Beyond address discovery, STUN responses also help clients infer their NAT type. By observing how the NAT maps addresses and ports across multiple requests, a client can determine whether it sits behind a full-cone NAT, a restricted-cone NAT, a port-restricted NAT, or a symmetric NAT. This matters enormously, because symmetric NATs break the direct peer-to-peer path that STUN enables.
It is worth contrasting STUN with TURN early, because the two are constantly mentioned together. A STUN server only helps peers discover each other's public addresses; it never touches media. A TURN server, by contrast, relays actual audio and video traffic when a direct connection fails. STUN is cheap and nearly always used; TURN is expensive and used only as a fallback.
How STUN Servers Fit Into the WebRTC ICE Process
The ICE framework, standardized in RFC 8445, is the orchestration layer that makes STUN useful. ICE stands for Interactive Connectivity Establishment, and its job is to gather every possible network path between two peers, test them in priority order, and select the first pair that works.
ICE candidate gathering happens in stages. First, the client collects host candidates, which are simply the local network interfaces of the device. Second, it sends STUN binding requests to every configured STUN server, producing server-reflexive candidates that represent the public mapped address. Third, if a TURN server is configured, it gathers relay candidates that represent addresses on the TURN server itself.
Once gathering completes, the candidates are exchanged through a signaling channel, and each peer begins connectivity checks. These checks are themselves STUN requests, sent peer to peer, which both verify reachability and perform UDP hole punching, the technique of sending outbound packets from both sides so that each NAT creates a mapping that permits inbound traffic from the other peer.
Here is where the STUN request sits in the overall flow:
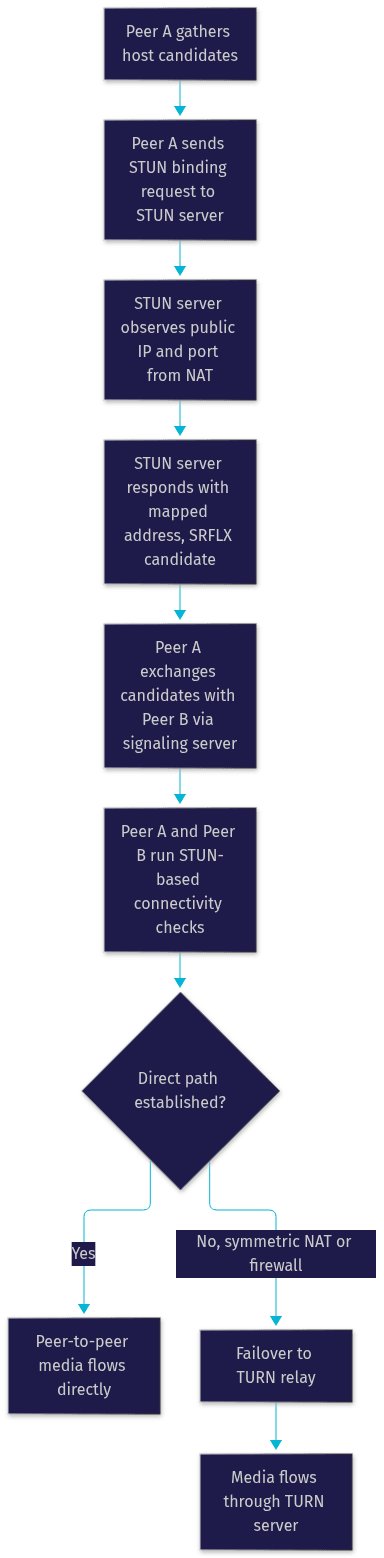
The key insight for developers is that STUN appears twice in this flow: once during gathering, to discover addresses, and again during connectivity checks, to verify and punch through NATs. When someone says their connection failed at the ICE stage, the problem is usually in one of these two STUN interactions.
Types of STUN Servers
STUN servers fall into two broad categories, and choosing between them is one of the first architectural decisions in any RTC project.
Public, free STUN servers are operated by large providers and community projects and require no authentication. Google's public STUN infrastructure, Twilio's NAT traversal endpoints, and Cloudflare's STUN service are the most commonly cited examples. These are excellent for development, prototypes, and small-scale production, but they come with no service-level agreement, and providers may rate-limit or discontinue them without notice.
Private, self-hosted STUN servers run on infrastructure you control. The dominant open-source implementation is coturn, a combined STUN and TURN server that runs on Linux and can be deployed on any virtual machine with a public IP address. Self-hosting gives you control over capacity, geolocation, and logging, at the cost of operating the service yourself.
Geography matters more than most developers expect. A STUN server in a different continent adds round-trip latency to every binding request and every connectivity check. For global applications, the standard practice is to deploy or select STUN servers close to your users, ideally in the same regions as your media infrastructure.
Choosing a Reliable STUN Server
Choosing a STUN server is a reliability decision, not a checkbox. The server is on the critical path of every connection your application makes, so a slow or dead STUN server directly increases connection setup time or causes outright failures.
Evaluate candidates against five criteria. Uptime: the server must be consistently reachable, because ICE gathering blocks on STUN responses or timeouts. Latency: binding requests should complete in well under 100 milliseconds from your users' regions. Protocol support: verify both IPv4 and IPv6 handling, since IPv6 peers often need different treatment than IPv4 peers behind NAT. Rate limits: public providers throttle aggressive clients, and a production app generating thousands of gathering requests can trip those limits. Resilience: servers behind DDoS protection and anycast networks survive abuse far better than single-instance community servers.
Testing responsiveness is straightforward. A simple ping verifies the host is up, but the real test is a STUN binding request, which confirms the service is actually answering on UDP port 3478. Several open-source STUN client tools can send a binding request and display the reflected address, which also confirms your own NAT behavior.
For production, always configure multiple STUN servers. ICE gathers from all of them in parallel, so if one is slow or unreachable, connection setup proceeds using the others. Two to three geographically distributed servers is the common production baseline.
Configuring STUN Servers in Common Platforms
Configuration always follows the same conceptual shape: you provide a list of STUN server URLs, and the platform's ICE agent handles gathering and connectivity checks. The differences are only in where that list lives.
Web Browsers and the WebRTC API
In browser applications, the STUN list is supplied as part of the ICE server configuration when creating a peer connection. Each entry is a URL with a stun scheme prefix, a hostname, and a port. The most common mistakes here are trivial but frequent: omitting the port, using an https prefix instead of stun, or pointing at a TURN-only endpoint with a stun prefix. All three produce silent gathering failures that only surface in ICE connection state logs.
Native SDKs on Android, iOS, and Unity
Native platforms expose the same concept through their respective APIs. Android's native WebRTC library accepts an ICE server configuration object when initializing a peer connection factory. iOS, whether through the native library or wrappers, follows the same pattern. Unity, typically via a WebRTC plugin, mirrors the browser configuration model. In every case, the list is set once at peer connection creation and cannot be changed afterward, so plan your server list before establishing connections.
Server-Side Signaling and Client Delivery
In production architectures, the STUN list is usually not hardcoded in the client. Instead, your signaling server delivers the current ICE configuration to each client during session setup. This lets you rotate servers, respond to outages, and tailor server lists to user geography without shipping app updates. A common pattern is for the token-issuing backend to include the ICE configuration alongside session credentials.
If you are building on a managed platform, this layer disappears entirely. VideoSDK's video calling SDKs handle STUN, TURN, and full ICE negotiation automatically, including network-adaptive streaming that adjusts bitrate and resolution when connectivity degrades. You never configure a STUN server at all; the platform's global infrastructure handles traversal for you.
Public STUN Server Lists: What to Watch Out For
Community-maintained STUN lists circulate widely on GitHub and blog posts, and they are genuinely useful, with caveats. Entries go stale constantly. Providers retire endpoints, change ports, or add authentication requirements, and the lists rarely get updated. A list that worked last year may be half dead today.
Treat any public list as a starting point for your own testing, never as a production configuration. Verify each endpoint with a binding test before relying on it, and re-verify periodically.
There are also legal and privacy considerations. Public STUN servers see your users' public IP addresses and request patterns. For regulated industries like healthcare or finance, routing user metadata through third-party infrastructure you have no agreement with deserves scrutiny. Self-hosting or using a contracted provider resolves this.
A short, currently reasonable starting list includes Google's public STUN endpoints, Cloudflare's STUN service, and Twilio's traversal infrastructure. Each is operated by a major provider with real infrastructure behind it, though none carries an availability guarantee for anonymous use.
Deploying Your Own STUN Server
Self-hosting a STUN server is one of the simpler infrastructure tasks in RTC, and coturn is the standard choice. The deployment process, described here in prose, involves a handful of clear steps.
First, provision a virtual machine with a public IP address, typically a small Linux instance since STUN is extremely lightweight. Second, install coturn from your distribution's package repository or build it from source. Third, configure the service to listen on UDP port 3478, the standard STUN port, and declare the machine's public IP so responses carry the correct address. Fourth, open the port in both the cloud provider's security group and the host firewall, for UDP specifically, since a firewall rule that only permits TCP is a classic silent failure. Fifth, verify with a STUN binding test from an external network.
Security hardening follows. If you only need STUN, disable the TURN relaying functionality to prevent the server being used as an open relay. Apply rate limiting so a single client cannot flood the service. Enable logging so you can observe request volume and detect abuse, and keep the software updated, since traversal services are exposed to the public internet by design.
Maintenance is light but real. Monitor reachability with an external probe, watch log volume for anomalies, and periodically confirm the reflected addresses are correct, since a misconfigured public IP declaration produces responses that break connectivity in confusing ways.
Troubleshooting Common STUN Issues
When connections fail, STUN is usually the first suspect, though not always the guilty party. Here is how to reason through the common failure modes.
Symmetric NAT is the fundamental limitation of STUN. A symmetric NAT assigns a different public port for every destination, so the address your STUN server discovered is not the address your peer sees. The direct path cannot form, and no amount of STUN configuration fixes it. The solution is TURN, which is exactly why ICE supports relay candidates. Mobile carrier networks are frequent symmetric NAT offenders.
Firewall or ISP blocking of UDP 3478 appears in corporate and some regional networks. The symptom is gathering timeouts for every STUN server while general internet access works fine. Testing from a different network, or over a VPN, quickly confirms the diagnosis.
Server unreachability splits into two causes: DNS failure and connectivity failure. If the hostname does not resolve, the problem is DNS. If it resolves but binding requests time out, the problem is routing, the port, or the server itself. Distinguishing these two early saves significant debugging time.
Inconsistent candidate types show up in ICE logs. If you see host candidates but no SRFLX candidates, STUN gathering failed entirely. If you see SRFLX candidates but connectivity checks fail, the NAT type or firewall is blocking the direct path. Reading ICE state transitions, from checking to failed, alongside the candidate types present, tells you which stage broke.
A practical verification checklist: confirm the server answers binding requests from an external network, confirm UDP 3478 is open end to end, confirm the URL scheme and port in your configuration, confirm SRFLX candidates appear in logs, and confirm both peers exchange candidates successfully through your signaling channel.
When to Switch to TURN or Hybrid Solutions
STUN succeeds for the majority of connections, with industry experience suggesting direct peer-to-peer paths form in roughly 70 to 80 percent of cases across typical consumer networks. The remaining fraction, concentrated in symmetric NATs, corporate firewalls, and strict ISP policies, requires a TURN relay.
The trade-off is cost. TURN relays carry actual media bandwidth, which makes it expensive at scale, while STUN costs almost nothing since it only handles small signaling exchanges. This is why the standard production pattern is hybrid: configure STUN servers for fast direct paths and a TURN server as a fallback, letting ICE automatically escalate only when direct connectivity fails.
This hybrid configuration is what every serious RTC deployment uses, and it is precisely what managed platforms operationalize for you. VideoSDK's infrastructure handles the full STUN and TURN hierarchy, along with cloud proxy and geo-fencing options for networks where even standard traversal is blocked, so the escalation from direct to relay happens without any client-side engineering.
Summary and Best Practices
The STUN server is a small service with an outsized role: it is the mechanism by which devices behind NATs learn their public addresses and form direct peer-to-peer connections. Get the fundamentals right and most of your connections will never need anything heavier.
The actionable checklist: always configure multiple STUN servers for redundancy, verify public endpoints before production use, prefer servers geographically close to your users, deliver ICE configuration from your signaling layer so you can rotate servers without app updates, watch for symmetric NAT failures and plan a TURN fallback, and consider self-hosting coturn when you need control, capacity guarantees, or privacy compliance.
For further reading, the VideoSDK documentation covers the full real-time communication stack, and the REST API reference covers server-side orchestration. The IETF's RFC 5389 and RFC 8445 remain the definitive specifications for STUN and ICE.
Definitions Glossary
STUN Server: A network service implementing the Session Traversal Utilities for NAT protocol that reflects a client's public IP address and port back to them, enabling NAT traversal without relaying media.
NAT Traversal: The set of techniques, including STUN, TURN, and UDP hole punching, that allow devices behind Network Address Translation to establish direct connections with external peers.
ICE Candidates: The network addresses gathered by the Interactive Connectivity Establishment framework, including host, server-reflexive, and relay candidates, that peers test in pairs to find a working connection path.
SRFLX Candidate: A server-reflexive candidate, the public IP and port a STUN server observes for a client, which the peer can use to attempt a direct connection.
TURN Server: A relay service that forwards actual audio and video media between peers when direct connectivity fails, used as a fallback within ICE alongside STUN.
UDP Hole Punching: A NAT traversal technique where both peers send outbound packets to each other simultaneously so their respective NATs create mappings permitting inbound traffic.
Key Takeaways
- A STUN server tells a device its public IP address and port as seen from the internet, which is the foundation of NAT traversal for WebRTC, VoIP, and SIP.
- STUN appears twice in the ICE process: during candidate gathering to discover addresses, and during connectivity checks to verify paths and perform UDP hole punching.
- Symmetric NATs break STUN's direct path model, which is why every production deployment needs a TURN relay configured as an ICE fallback.
- Public STUN servers are fine for development, but production requires verified endpoints, geographic distribution, and redundancy across at least two or three servers.
- Managed platforms like VideoSDK eliminate this entire layer, handling STUN, TURN, and ICE negotiation automatically across ten-plus platform SDKs with network-adaptive streaming built in.
Conclusion
The STUN server is the quiet workhorse of real-time communication: a tiny protocol exchange that makes direct peer-to-peer media possible for the majority of users. Understanding how it discovers public addresses, where it sits in ICE gathering, and why it fails on symmetric NATs gives you the debugging intuition that separates smooth deployments from frustrating ones. If you would rather never think about STUN configuration, TURN capacity, or ICE logs again, VideoSDK's video calling SDKs handle the full traversal stack for you, and you can start free at app.videosdk.live/login. What are you building with real-time communication? Drop a comment, I'd love to hear what kind of connectivity challenges you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ