


CDN HLS streaming is the delivery of HTTP Live Streaming video through a content delivery network, where edge servers cache HLS playlists and media segments close to viewers. This combination cuts startup time, absorbs massive audience spikes, and reduces origin load. If you are building live video in 2026, understanding how a CDN caches and serves HLS is non-negotiable, and this guide walks through the full delivery chain, low-latency options, and production configuration.
Latency is the silent killer of live video products. A viewer watching a game-winning goal on social media seconds before your stream shows it is a churn event, not a technical footnote. Standard HLS delivered without a CDN routinely runs 15 to 30 seconds behind live, and every hop between your origin server and the viewer adds more.
CDN HLS streaming exists to solve exactly this class of problem. By pushing your HLS playlists and media segments to edge servers physically near your audience, a CDN shortens the delivery path, absorbs traffic spikes that would flatten a single origin, and gives you the caching and security controls that raw HTTP delivery cannot. By the end of this article you will understand the full architecture, the configuration decisions that matter, how low-latency HLS changes the picture, and how to pick a provider.
What is CDN HLS Streaming?
HTTP Live Streaming, or HLS, is defined as an adaptive bitrate streaming protocol created by Apple that breaks video into short media segments and describes them in text-based playlist files. A player downloads a playlist, chooses a rendition matching its available bandwidth, fetches the listed segments, and stitches them into continuous playback. Because it rides on plain HTTP, HLS passes through firewalls, proxies, and standard web infrastructure without special servers.
A CDN, or content delivery network, is a globally distributed fleet of edge servers that cache content near end users. In CDN HLS streaming, the CDN sits between your origin (where segments and playlists are produced) and every viewer. The first request for a playlist or segment pulls it from the origin; subsequent requests for the same object are served from the edge cache.
Understanding CDN HLS streaming means understanding this division of labor: the origin encodes and packages, the CDN distributes and caches, and the player adapts. The result is that one origin server can serve millions of concurrent viewers, because the vast majority of requests never reach it.
Benefits of Using a CDN for HLS
The core value of a CDN for HLS delivery is scale without origin pain. A single live event can generate millions of segment requests per minute, and a well-tuned CDN absorbs nearly all of them at the edge through high cache-hit ratios.
Edge caching applies to every object type in the HLS chain. The small text playlists and the larger media segments are both cached at edge locations, so viewers in different regions get fast first-byte times and smooth mid-stream playback. Because segments are immutable once published, they cache aggressively, while playlists use short TTLs to stay fresh.
Security is another major benefit. Most CDNs provide geo-blocking to restrict delivery by region, signed URLs and token authentication to prevent playlist theft and hotlinking, and origin shielding to hide the origin from direct attack. Finally, cost efficiency improves because cache hits are billed at edge delivery rates rather than triggering repeated origin egress, and a high cache-hit ratio directly lowers your bill.
How CDN HLS Streaming Works
CDN HLS streaming works by intercepting every player request at the nearest edge server, serving cached objects instantly, and fetching from origin only on a cache miss. The architecture is simple in principle, but the caching rules for each object type are where correctness lives.
Architecture Overview
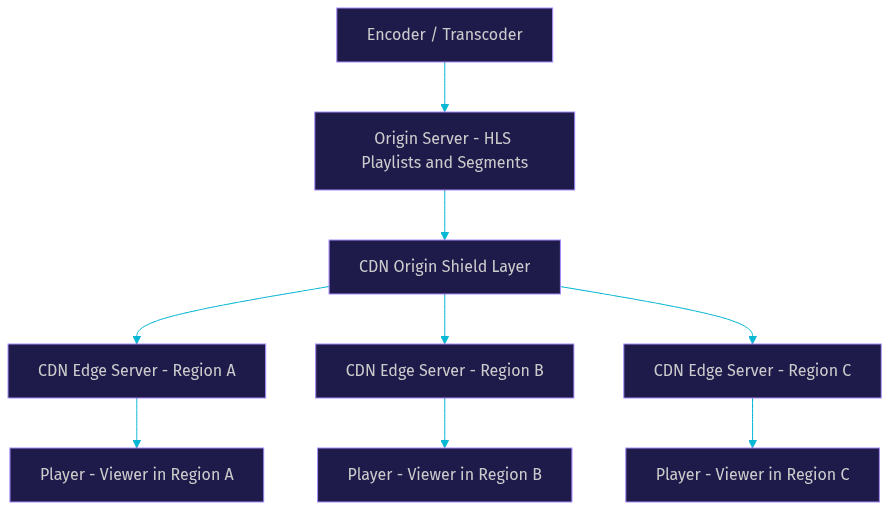
The diagram below shows the full delivery chain, from the encoder producing HLS at the origin to the player consuming it at the edge.
Request Flow
When a player starts a stream, it first requests the master playlist, which lists available renditions at different bitrates. The edge server checks its cache; on a miss, it forwards to the origin shield layer, which checks its own larger cache before touching the origin. The chosen variant playlist is then fetched, followed by the media segments it references.
Each segment request follows the same cache-lookup path. Because thousands of viewers in the same region request the same segment within seconds of each other, the first request warms the cache and the rest are served from the edge. This is why a single origin can support enormous audiences: the CDN collapses a flood of duplicate requests into a handful of origin fetches.
Cache-Control Strategies
The single most important CDN HLS configuration decision is differentiating TTLs by object type. Playlists change constantly during a live stream, so they need short cache times, typically a few seconds to a few minutes, or viewers will hold stale playlists and stall. Media segments are immutable once written, so they can be cached for hours or days. A common production pattern is to set a very short TTL on playlist responses and a long TTL on segment responses, keyed by file extension. Getting this backwards is the number one cause of frozen live streams.
Key Configuration Considerations
Configuring a CDN for HLS correctly involves four areas: naming, query parameters, security, and origin protection. Each one has production-level gotchas that quickstarts skip.
Playlist and Segment Naming Conventions
HLS objects are identified by extension, and your CDN cache rules will almost certainly key off them. Playlists use the m3u8 extension, while media segments use the ts extension for MPEG transport streams or the m4s extension for fMP4 segments used by low-latency HLS and CMAF packaging. Some setups also serve progressive mp4 assets alongside the segment tree. Keeping a clean, consistent naming scheme lets you write simple, reliable cache rules: short TTL for m3u8, long TTL for ts and m4s, and no caching for anything dynamic. Avoid query strings in segment URLs themselves, because many CDNs treat differing query strings as distinct cache keys and fragment your hit ratio.
Query Parameter Whitelisting
Low-latency HLS players append special query parameters to playlist requests, including the media sequence number, the part index, and a skip directive that tells the server to return only newly added playlist lines. If your CDN strips or ignores these parameters, LL-HLS breaks in subtle ways: players receive full playlists instead of deltas, or receive the wrong partial segment. The fix is to whitelist these specific parameters in your CDN configuration so they pass through to the origin and are handled correctly, while still excluding random tracking parameters that would fragment the cache.
Secure Token Generation
For protected content, generate a signed token server-side, typically a JWT or an HMAC-based token containing an expiry timestamp and allowed path scope, and append it to playlist and segment URLs. The CDN validates the token at the edge before serving, which means unauthorized requests are rejected without touching the origin. Keep token lifetimes aligned with session length, and remember that playlists refresh continuously, so tokens must remain valid for the whole viewing session or be refreshed by the player. Never embed long-lived secrets in client-side URLs.
Origin Shielding and Failover
Origin shielding adds an intermediate caching tier between the edge and your origin. All edges in a region fetch through the shield, so even a cache miss storm across many edge locations collapses into one request per object at the shield. During a live event spike, this is the difference between a stable origin and an overloaded one. Configure failover so that if the primary origin is unreachable, the CDN retries against a backup origin, keeping the stream alive through infrastructure hiccups.
Low-Latency HLS (LL-HLS) via CDN
Low-latency HLS is Apple's extension to the protocol that reduces glass-to-glass latency from the traditional 15 to 30 seconds down to roughly 2 to 5 seconds. It differs from standard HLS in three key ways: segments are broken into smaller partial segments that can be delivered before the full segment completes, playlists can be requested with delta queries that return only new lines, and the protocol is designed to take advantage of HTTP/2 push, where the server proactively sends new segments the player will need next.
Optimizing CDN HLS streaming performance for LL-HLS requires the edge to handle these behaviors natively. The CDN must forward the media sequence number, part index, and skip parameters correctly, block-on-playlist requests that hold connections open until new content appears must not be buffered or timed out by the edge, and HTTP/2 must be enabled end to end. Partial segments, delivered as m4s files under CMAF packaging, need the same immutable, long-TTL caching treatment as full segments.
A practical configuration checklist for LL-HLS on a CDN edge looks like this: enable HTTP/2 between edge and player, whitelist the LL-HLS query parameters, set near-zero TTLs on live playlists with block-on-playlist support, cache partial segments aggressively, and verify that edge connection timeouts exceed the block-on-playlist hold time. Test with real players, not just curl-style fetches, because the failure modes only appear in playback.
Common Pitfalls and Troubleshooting
Most CDN HLS streaming failures trace back to a handful of misconfigurations. Stale playlists caused by overly long TTLs produce frozen streams where the player keeps requesting segments that no longer exist in the current playlist. Segment-size mismatches, where the encoder changes segment duration mid-stream without the CDN or player adapting, cause buffering and stalls as the player's timing assumptions break.
Misconfigured query-parameter whitelisting is the classic LL-HLS trap: everything works in testing from one region, then fails at scale because a tracking parameter fragments the cache or a required parameter is stripped. When debugging, use three tools together: CDN logs to confirm cache-hit ratios and TTL behavior per object type, the player console to see which requests fail or stall, and a network waterfall in browser developer tools to spot slow first-byte times that point to origin fetches instead of edge hits. A healthy live stream shows hit ratios in the high nineties for segments; anything lower means your cache rules need attention.
Choosing the Right CDN Provider for HLS
Evaluate HLS CDN providers on five criteria: edge network coverage in your audience's regions, HLS-specific features like extension-aware caching and block-on-playlist support, native LL-HLS support, pricing model (bandwidth versus request-based, since segment-heavy HLS generates enormous request counts), and support SLA for live events.
Cloudflare offers strong global coverage and a generous free tier, with Stream delivery features suited to HLS, though advanced LL-HLS behaviors need verification on your plan. Akamai is the enterprise incumbent with the deepest HLS feature set, including sophisticated origin shielding and adaptive delivery, at enterprise pricing. Gcore provides strong coverage in regions often underserved by the big two, competitive per-traffic pricing, and native low-latency HLS support. The right answer depends on where your viewers are and how request-heavy your packaging is.
Real-World Use Cases
Live sports broadcasting is the flagship CDN HLS use case: millions of concurrent viewers, regional spikes, and a hard requirement for the lowest latency the protocol allows, which makes LL-HLS over a shielded CDN the default architecture.
E-learning platforms delivering adaptive bitrate lectures rely on CDN HLS streaming for a different reason: students on unpredictable home connections need ABR renditions served reliably, and edge caching keeps bandwidth costs sane across large cohorts. Large-scale live shopping events combine both patterns, adding interactive chat and purchase actions where even a few seconds of stream lag desynchronizes the host's pitch from the comment feed. For these interactive scenarios, consider pairing HLS delivery with a sub-second interactive streaming layer, such as VideoSDK's interactive live streaming, which keeps audience interaction real-time while HLS handles one-to-many scale.
Best-Practices Checklist for Production
- Set short TTLs on m3u8 playlists and long TTLs on ts and m4s segments.
- Enable origin shielding before any large live event.
- Whitelist LL-HLS query parameters and strip tracking parameters.
- Use signed tokens with session-aligned expiry for protected streams.
- Enable HTTP/2 end to end for low-latency HLS.
- Monitor cache-hit ratios per object type, not just aggregate.
- Configure a backup origin for failover.
- Load-test with realistic player behavior, including mid-stream joins.
Definitions Glossary
HLS (HTTP Live Streaming): Apple's adaptive bitrate protocol that splits video into segments described by text playlists, delivered over plain HTTP. Players select renditions based on available bandwidth.
CDN Edge Server: A cache server in a content delivery network located near viewers, serving cached HLS playlists and segments without contacting the origin.
Cache-Control TTL: The time-to-live a CDN honors for a cached object. Playlists need short TTLs to stay fresh; immutable segments cache for long periods.
Low-Latency HLS (LL-HLS): An HLS extension using partial segments, delta playlist queries, and HTTP/2 push to cut live latency to roughly 2 to 5 seconds.
Origin Shielding: An intermediate CDN caching tier between edge servers and the origin that collapses cache-miss storms into a single origin fetch per object.
Adaptive Bitrate (ABR): The player-side mechanism that switches between HLS renditions of different quality as network conditions change.
Key Takeaways
- CDN HLS streaming places edge caches between your origin and viewers, collapsing millions of duplicate requests into a handful of origin fetches.
- Differentiate cache TTLs by object type: short for playlists, long for immutable segments; getting this wrong freezes live streams.
- Low-latency HLS reduces glass-to-glass delay to roughly 2 to 5 seconds using partial segments, delta queries, and HTTP/2 push, but requires CDN edge support for its query parameters.
- Origin shielding and token authentication are the two features that keep your origin alive and your content protected during spikes.
- Choose a CDN provider based on edge coverage in your audience's regions, native LL-HLS support, and a pricing model that accounts for HLS's high request counts.
Conclusion
CDN HLS streaming is the backbone of scalable live video in 2026: the protocol provides adaptive delivery over plain HTTP, and the CDN provides the global edge caching, shielding, and security that make it survive real audiences. The configuration details, TTLs, query whitelisting, token auth, and LL-HLS edge support, are where streams either run flawlessly or stall in front of millions. Start a trial with your shortlisted CDN, test low-latency HLS with real players, and monitor cache-hit ratios from day one. If your use case needs genuine real-time interaction alongside HLS scale, explore VideoSDK's interactive live streaming or grab the code samples and start building. What are you building with HLS delivery? Drop a comment, I'd love to hear what kind of streaming use case you're working on.
Free $20 Balance for AI Voice Agents & Video Calls
FAQ